Product
Your cybersecurity team, on a single platform.
Our own platform and AI specialists coordinated by Aegis. Indene connects what you already use, works every day and shows the result in money terms.
- Every company isolated from day one
- Credentials can stay on your network
- Every action logged, with who approved it
- Trust page
How it works
From the first connector to reporting back.
You connect once. After that, the team works in the background, with no one needing to open the screen, and each person gets their part.
You connect
Prove the domain, link the directory and the tools with read-only credentials. Some can be collected by an agent inside your network.
The team works
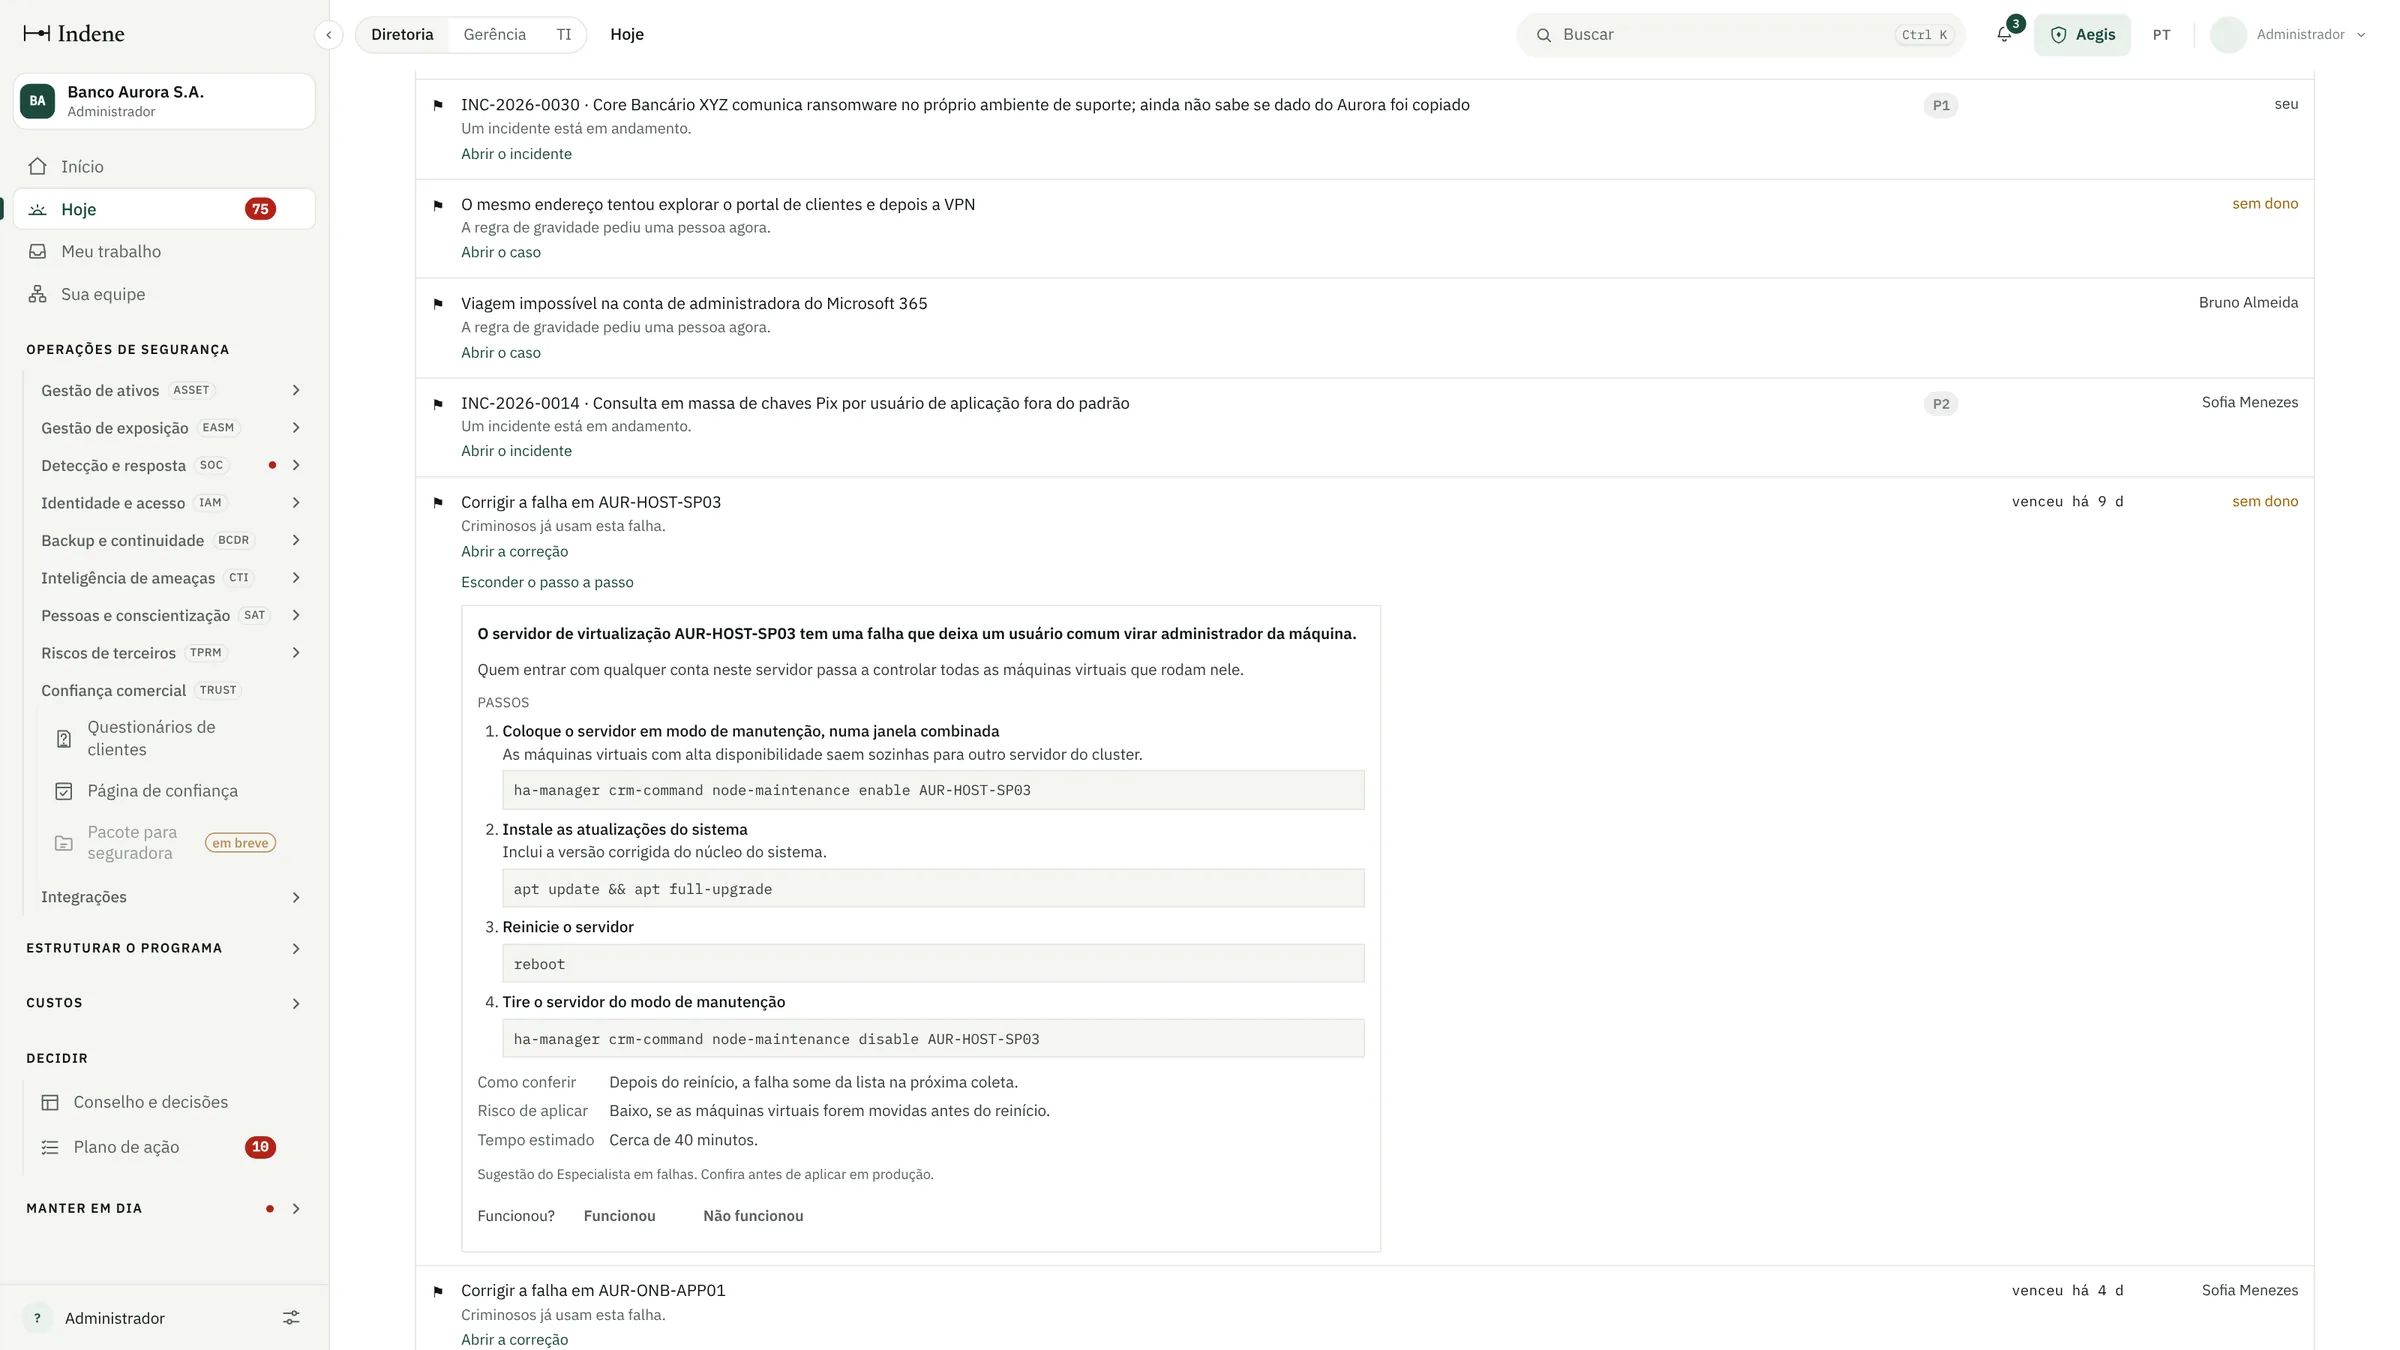
The AI specialists triage alerts, check backups, look at the company from the outside and prepare the fixes.
You receive
IT gets the daily queue, management the weekly summary and the board the monthly report, with serious alerts right away.
What changes
IT fixes, the platform checks on its own at the next collection and attaches the proof. Risk in money terms shows the work done.
One platform, three conversations
Each person opens to what is theirs.
The same company, three readings. The language changes with the reader: consequence and decision for the board, deadline and owner for management, the next step for IT.
- Board
Are we protected? What does it cost? What do I approve?
Possible loss in money terms, as a range with the confidence alongside, what the team did in the period and the decisions waiting for your approval.
Every month, plus serious alerts right away - Management
Is the plan moving? What is late? Are we ready for the audit?
The action plan with owner and deadline, incidents in progress, evidence about to expire and readiness for the inspection.
Every week - IT
What do I do first today? How do I fix it?
The “Today” queue, in risk order, with what it is, where it is, why it matters and the step by step for each fix.
Every day
The modules
Ten operations sectors, and the program around them.
The product menu follows the way a security team is organized. Each sector has its AI specialist and the market acronym next to its name.
- ASSET
Asset management
The unified inventory: every machine with an owner, process and protection, and an alert when an unknown one shows up.
- EASM
Exposure management
What an attacker sees from your domain alone, vulnerabilities per asset, the fix queue and penetration tests.
- SOC
Detection and response
Alerts from every source in one hub, triaged by AI, and the incident record with the legal deadlines running.
- IAM
Identity and access
Who can do damage and what protects that person: accounts without a second factor, forgotten or privileged, and suspicious logins.
- BCDR
Backup and continuity
Copies checked against the 3-2-1 rule and the restore test that tells how long each machine takes to come back.
- CTI
Threat intelligence
Threats out there that already reach your company: vulnerabilities exploited in the wild and leaked passwords.
- SAT
People and awareness
Training and testing employees against email scams.
- TPRM
Third-party risk
Critical vendors linked to the processes they support.
- TRUST
Commercial trust
Customer questionnaires answered with evidence and the public trust page.
- API
Integrations
The connected tools, what each one covers and the request for a new connector.
The security program, around operations
Structure the program
Risk scenarios, processes, standards and policies, with the Statement of Applicability.
Decide
Board and decisions with the effect in money terms, and the action plan with owner and deadline.
Keep up to date
Audits with findings and the obligations calendar.
Costs
Contracts, spending, budget and the return of each control. A separately contracted module.
The first hour
A snapshot of your company, without installing anything.
The entry assessment can stop and pick up where it left off. Only the first three steps are required; the snapshot comes on screen and as a PDF.
Tell us about the company
Sector, size and revenue, always as ranges. About three minutes.
Prove the domain
A DNS record shows the domain is yours. About five minutes.
See it from outside
The passive scan runs on its own, without trying to break into anything.
Connect what you can
The directory and the backup, if you want, and ten questions in owner language.
What the snapshot shows
- What is exposed from the outside
- What is fine
- What we do not know yet: a gap is a missing source, not a bad grade
- The first ten actions, which become the first lines of the “Today” queue
- The value in money terms, as a range with the confidence, when there is data for it
What we do not negotiate
Built to be checked.
- Every value is a range, and no number appears without the confidence alongside
- Every piece of evidence has a source, date and author, and is never edited
- The audit trail is immutable, with who did it and who approved it
- Every company isolated from day one
- One assessed control answers every standard linked to it
- AI proposes; what cannot be undone waits for a person
- Portuguese, English and Spanish across the whole interface
- Invitation-only access, with admin, executive, manager, operator, consultant and auditor roles
Frequently asked questions
What people ask before the assessment.
Do I need to replace any tool?
No. Indene reads the tools your company already uses, with read-only credentials. Whatever has no connector yet comes in by request or by manual entry.
Do I need a security team?
No. Without a team, the AI team watches and prepares, your IT executes step by step and you approve. With a team or a CISO, Indene brings it all into a single view and takes the repetitive work off the table.
Does Indene replace my antivirus or my firewall?
No. It reads what those tools see, triages the alerts, proves which controls work and turns that into priority and risk in money terms.
How long does it take to start?
The entry assessment takes about an hour and requires installing nothing: company data, domain proof and the outside view. Connecting the directory and the backup is optional and adds a few minutes.
How do I get into the platform?
By invitation. There is no open sign-up: the account is created from the assessment, with the roles your company defines.
See your company through Indene’s eyes.
Book the assessment: in about an hour, you know how the company looks to an attacker and what to do first.