Product · Evidence and proof
Proof, not promises.
The control is Indene’s unit. Each one carries the proof that it works, with date, source and author, and answers every standard linked to it at once.
- DeclaredThe company states it, and a document backs it up: the policy, the procedure, the contract.
- EvidencedTool data shows the control working: the backup ran, the machine is protected.
- ValidatedA test exercised the control: a timed restore, a pentest or an attack simulation.
- Every company isolated from day one
- Credentials can stay on your network
- Every action logged, with who approved it
- Trust page
The levels of proof
The stronger the proof, the more reliable the number.
A control sits at the level of its best evidence that is still valid. Old evidence loses weight and shows as expired, and the administrator is notified.
Declared
The company states it, and a document backs it up: the policy, the procedure, the contract.
Evidenced
Tool data shows the control working: the backup ran, the machine is protected.
Validated
A test exercised the control: a timed restore, a pentest or an attack simulation.
Design and effectiveness are two scores per control, and never become an average.
Where proof comes from
Evidence arrives through several paths.
From connectors
Data collected from your tools becomes evidence with date and source, with no file to attach.
From checked fixes
IT fixes, the platform checks at the next collection and closes the fix with the proof attached.
From documents
AI reads the policy or procedure, suggests the score and quotes the passage with its page. A person accepts, edits or rejects.
From tests
Restore tests, pentest reports and attack simulations raise the control to validated.
From people
Evidence requests between teams and audits, with owner and deadline.
Evidence is never edited: a correction creates a new one that replaces the previous, and the previous stays visible in the trail.
The standards
One control, ten standards.
One assessed control answers every standard linked to it, with full or partial coverage. No more one spreadsheet per standard.
- CMN Resolution 5.274 and BCB 538
- ISO/IEC 27001:2022
- CIS Controls v8.1
- NIST CSF 2.0
- SOC 2
- PCI DSS 4.0
- LGPD
- GDPR
- ISO/IEC 27701
- HIPAA Security Rule
Ready for the audit
- Statement of Applicability as a PDF, with the justification for each control that does not apply
- Policies with version, approval and employee acknowledgment
- Audits with findings and the obligations calendar
- A countdown to the inspection
Customer questionnaires
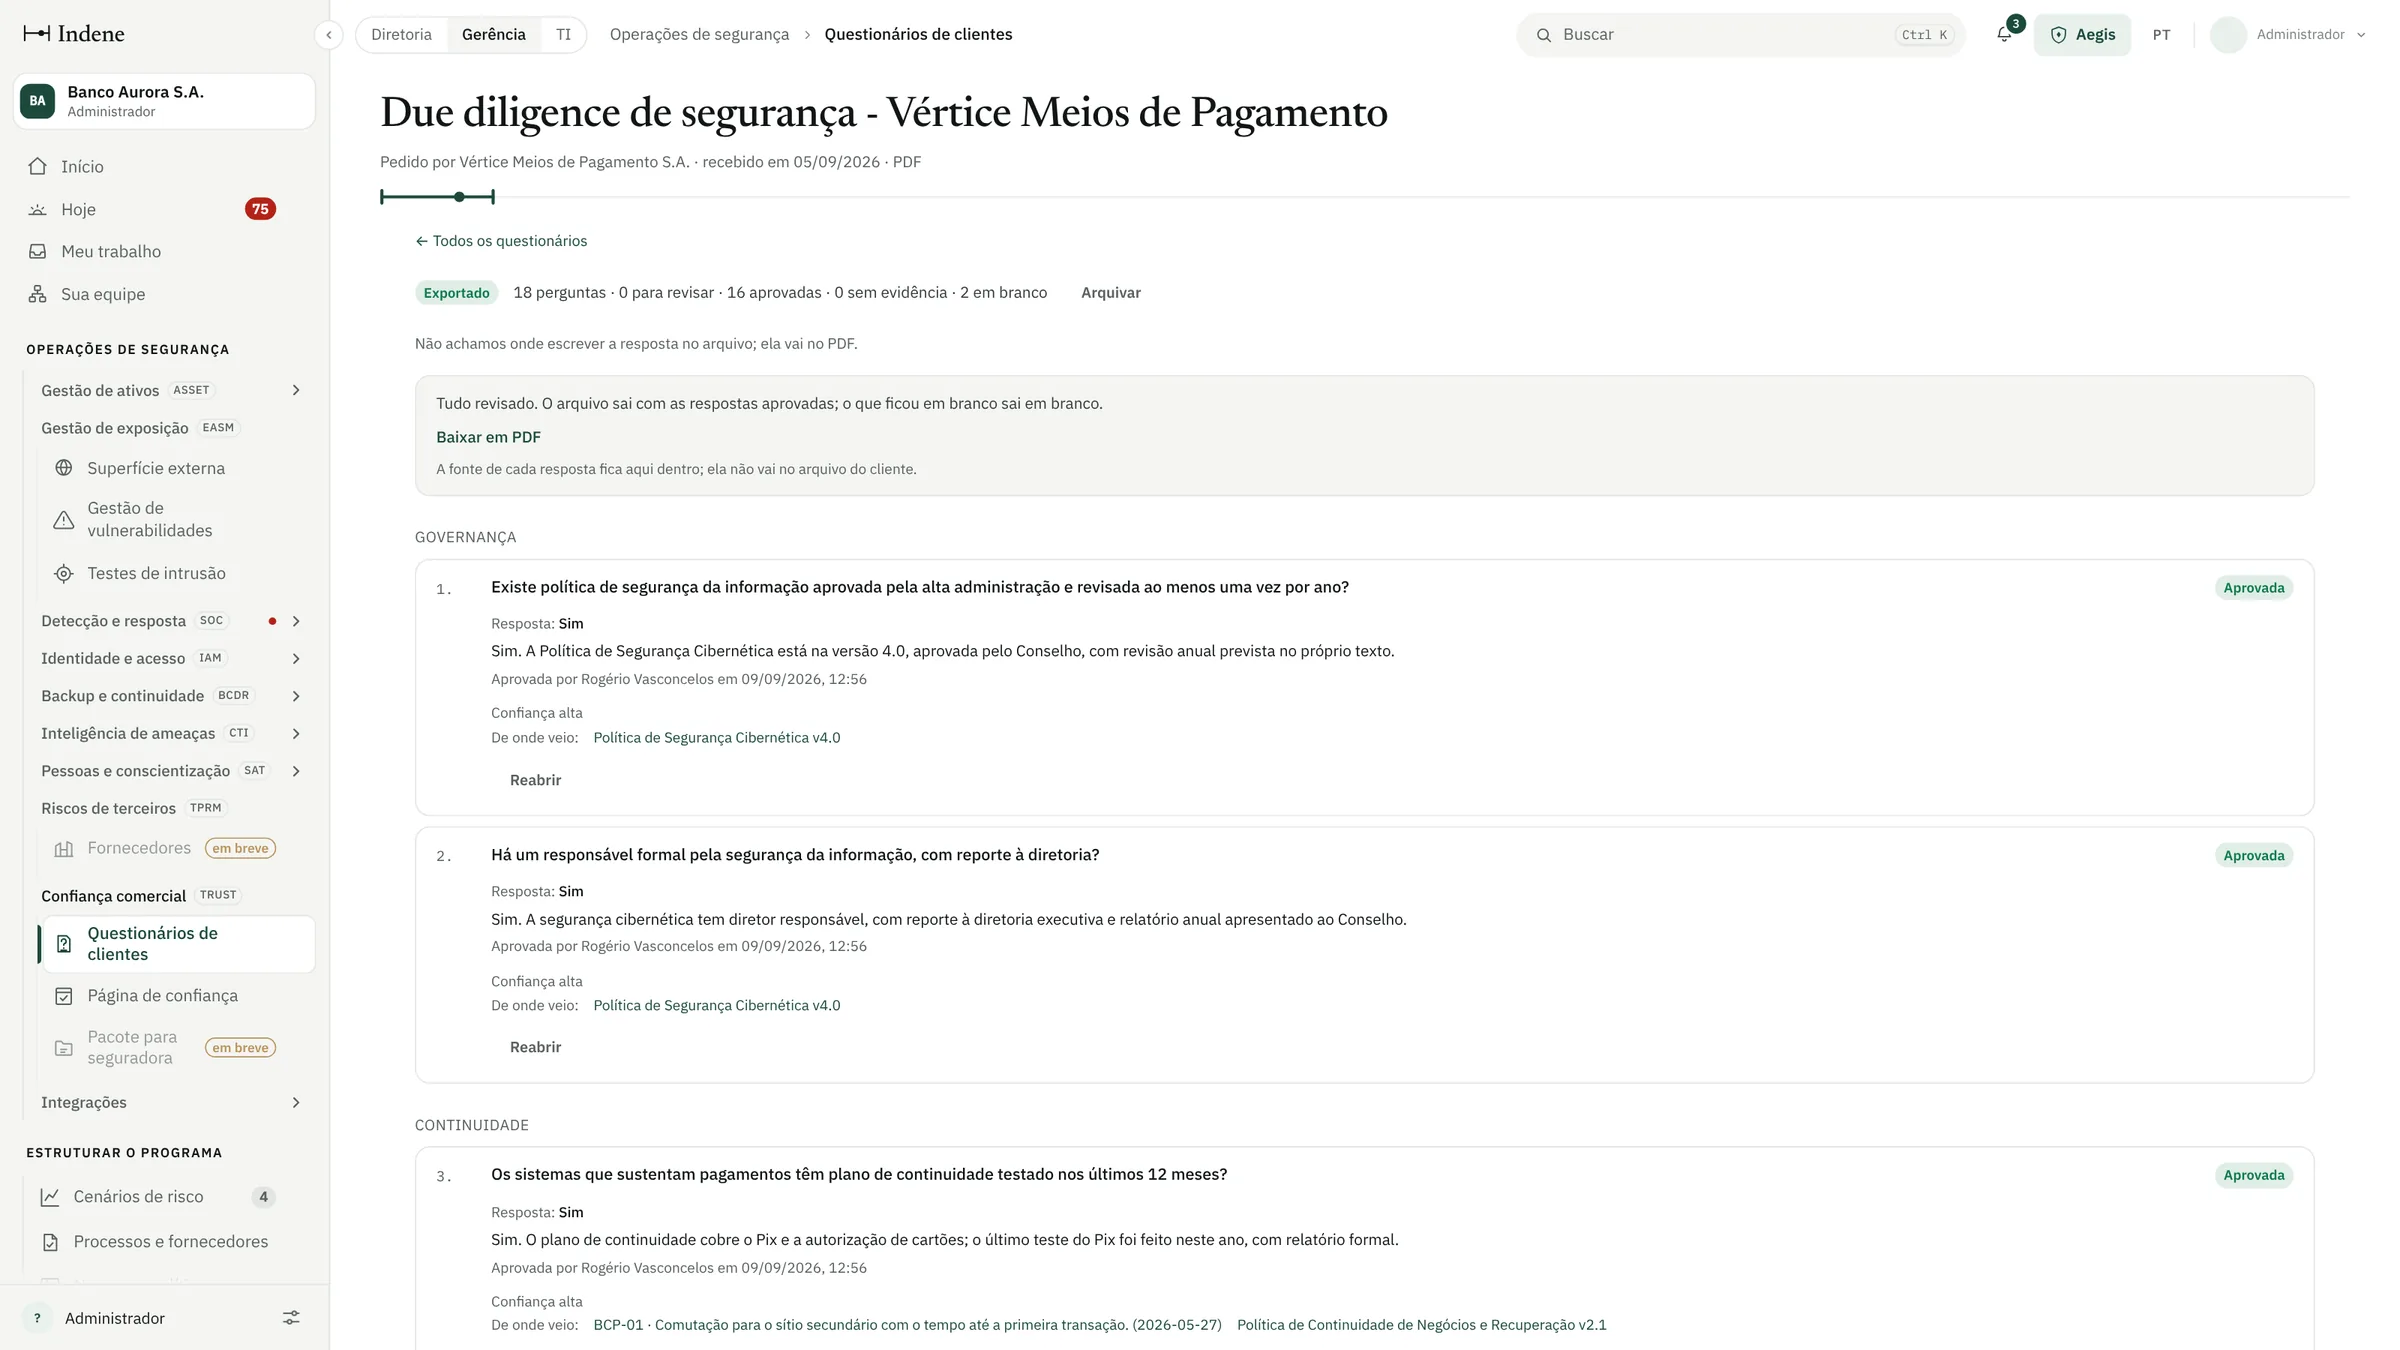
The large customer’s questionnaire, answered with the evidence.
Upload the file you received, as a spreadsheet, document or PDF. The AI specialist proposes each answer with the evidence behind it, you review and download the same file, filled in.
- An answer without a valid source becomes “no evidence”, however convincing the text looks
- Nothing goes out without review, and approval records who approved it and when
- Sources stay on the platform and do not go into the customer’s file
- Every approved answer goes into the library and is reused in the next questionnaire
Trust page
Your posture, published with proof.
A public page for your company to show customers and partners what you do, item by item, with only what you choose to publish.
Only current proof
Featured controls appear with evidenced or validated proof, and come down on their own when the proof expires.
Standards and policies
The standards followed and the approved policies. "Certified" only appears with the report published.
Documents on request
The visitor asks, your company approves before sending.
Badge and summary
A badge for your website and a PDF summary. Nothing negative is published.
Tests
The strongest proof is the one that was tested.
Pentest with report
AI reads the report and proposes the findings, linked to controls. A person confirms each one, and the retest proves the fix.
Timed restore
The proof becomes “we are back in so many hours”, as a range, and feeds the ransomware scenario. One critical machine at a time, in rotation.
Control validation
Proof from simulated attacks shows what your defense stopped and its effect in money terms.
Frequently asked questions
About proof and compliance.
Which standards does Indene cover?
Ten: CMN 5.274 and BCB 538, ISO/IEC 27001:2022, CIS Controls v8.1, NIST CSF 2.0, SOC 2, PCI DSS 4.0, LGPD, GDPR, ISO/IEC 27701 and HIPAA. One assessed control answers all those linked to it.
Can AI make up evidence?
No. AI suggests and quotes the source, and a person accepts or rejects. A questionnaire answer without a valid source becomes “no evidence”.
What happens when evidence gets old?
It loses weight, shows as expired and the administrator is notified. On the trust page, the item comes down on its own.
Does Indene certify my company?
No. Indene organizes and proves the controls for your audit. Certification remains with the certification body, and the trust page never says “verified by Indene”.
Close your next contract with the proof in hand.
Book the assessment and see your controls, the standards covered and what is left to prove.